I implemented passkeys for the first time, and WebAuthn turned out to be the easy part. Everything around it was harder, account recovery most of all.
The API is a weekend of work
Registration ceremony, authentication ceremony, verify the signature, store the credential. The spec is dense, but the libraries are good now. The server generates a challenge, the browser asks the authenticator to sign it with a private key that never leaves the device, and you verify that signature against the public key you stored at registration. That part is well understood and well supported.
Then the real project starts
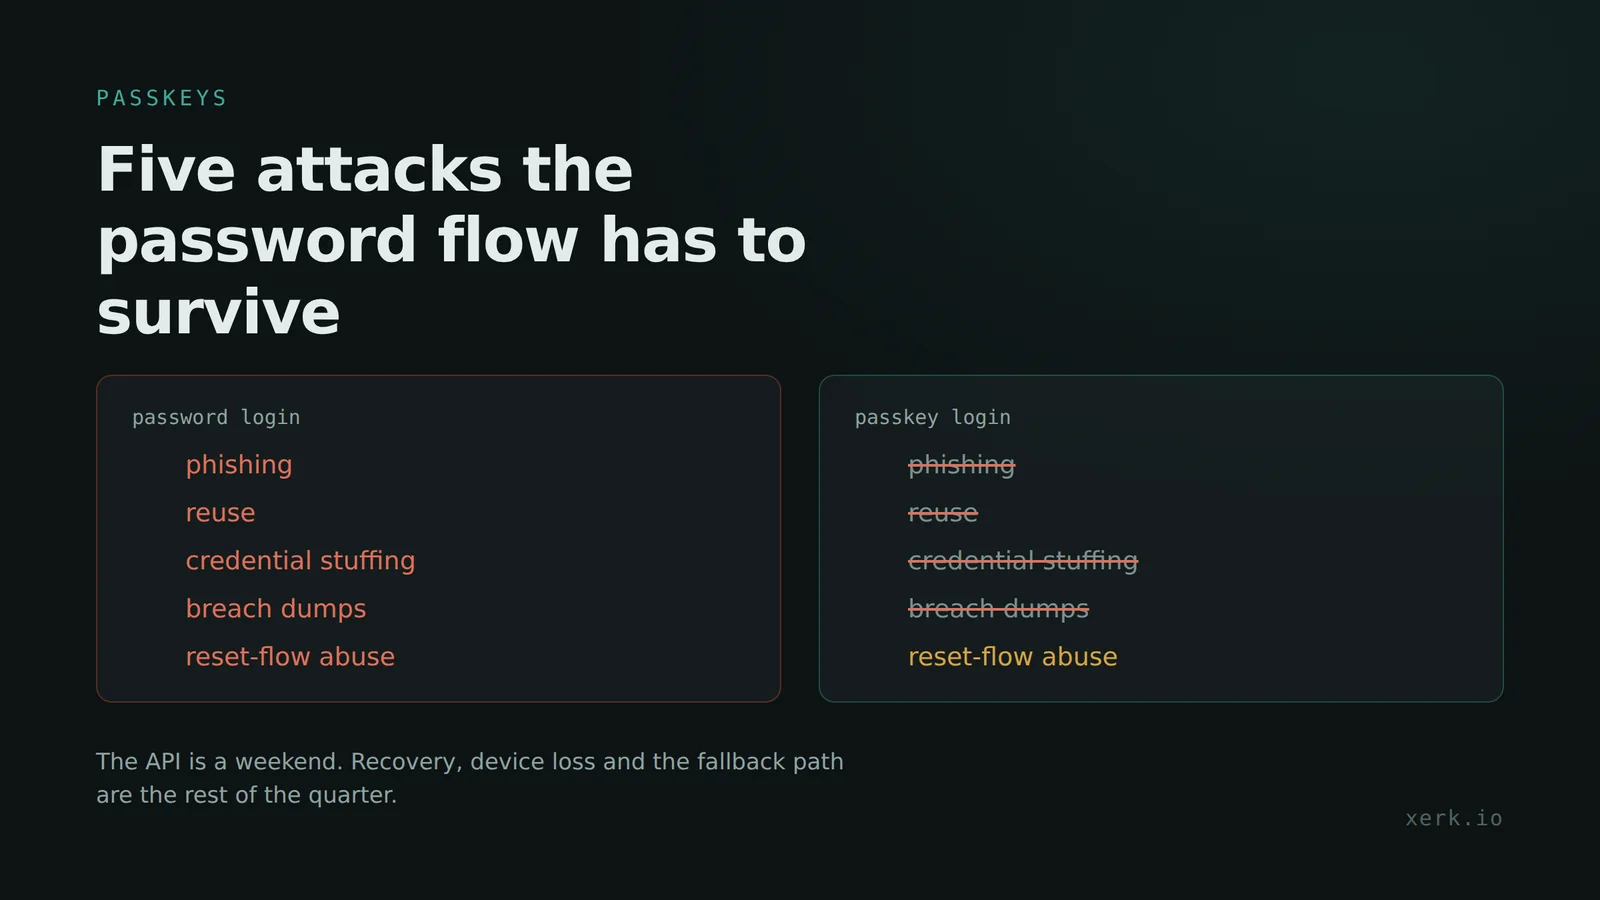
What happens when the user loses the device? What does account recovery look like when there's no password to reset? Do you keep the password as a fallback, and if you do, did you improve security or just add a second door to the same room?
That last question ate two weeks of design discussion. A passkey next to a weak password fallback is a strong lock on a house with a broken window. Attackers go for the weakest way in, so you're only as secure as your worst login path.
Where we landed
We went passkeys first, with an email magic link for recovery, and dropped passwords entirely for new accounts.
Support tickets about logins went down, and nobody asked where the password field went. Users adapt faster than product managers fear. If you're still all passwords in 2026, the blocker probably isn't technical.
Building something like this?
I'm Ahmed Mamdouh, a senior full-stack and AI engineer. I reply within one working day.